Specialized Skill Training - GRC Fundamentals
Build a practical foundation in cybersecurity governance, risk, and compliance.

Learn with
Hafiz Ali Mansoor Elahi
Course instructor
Certificate
Included
Starting from
Join anytime
Level
beginner
Duration
1m
Language
Urdu
Lessons
1
How you attend
Join anytime
No fixed start date or time. Enroll and attend on-site whenever you are ready.
Faisal Town Block C, Lahore
Faisal Town Block C, Lahore
≈ PKR 40,000.00
One-time payment · Ongoing access
- Format
- On-site
- When
- Join anytime
- Venue
- Faisal Town Block C, Lahore
- Address
- Faisal Town Block C, Lahore
This course includes
- 1 lessons
- Lifetime access
- Learn on desktop and mobile
- Certificate of completion
- 30-day refund request window
Guests can add to cart — sign in at checkout
Secure Checkout
Have a coupon?
Enter your code during checkout
Instructor
Hafiz Ali Mansoor Elahi
Course instructor
15+
Years exp.
Verified
Instructor
Course overview
About this course
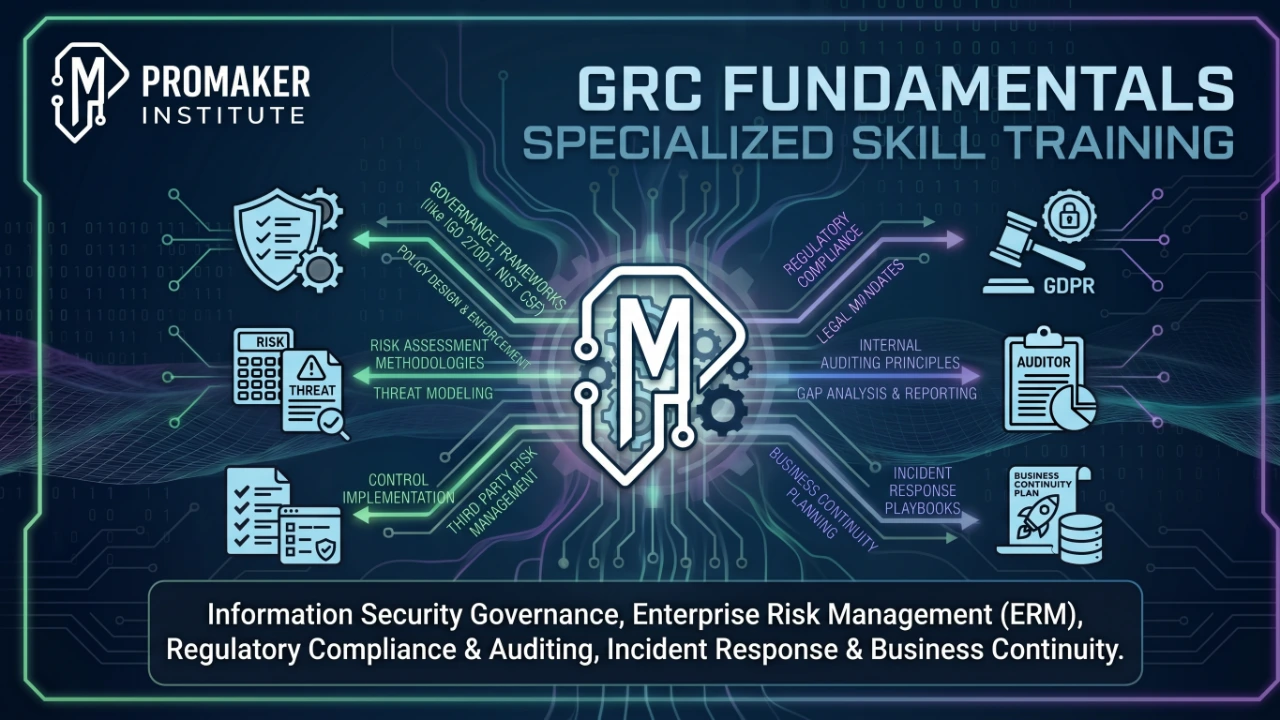
This specialized training track is designed for IT professionals, security analysts, and system administrators transitioning into cybersecurity management and compliance. The curriculum bridges the gap between technical operations and organizational leadership, focusing on designing, implementing, and auditing enterprise-grade security postures. Through hands-on labs and enterprise tool integrations, students will conduct simulated audits and translate technical vulnerabilities into business risk metrics. Graduates leave with a personalized portfolio of deployable security policies and audit checklists ready for enterprise use.
What you'll learn
Curriculum preview
1 sections · 1 lessons · 1m
1. Course Onboarding & The GRC Landscape
1 lesson · 696h 30m
- 1.The Business of Security & Mindset Shift696h 30m
Skills you will learn
- Cybersecurity
- Specialized Skill Training
- GRC Fundamentals
Student reviews
Be among the first to review
Verified learner feedback will appear here.
Your learning path
Course Curriculum
Browse the lesson outline. Full topic breakdowns unlock after enrollment.
Verified feedback
Student Reviews
No published reviews yet
Sign in after enrolling to leave a verified review.
Trusted reviews only
Reviews from enrolled learners will appear here once published, so every rating reflects a real learning experience.
Need to know
Frequently asked questions
Do I need programming or coding experience for this course?
No, this course focuses on governance, risk frameworks, and compliance auditing rather than coding or technical engineering.
Will this course prepare me for external professional certifications?
Yes, the curriculum provides a strong foundational understanding that aligns with core concepts tested in industry certifications like CISA, CRISC, and ISO 27001 Lead Auditor.
Are the enterprise tools used in the course free?
We utilize free trials and sandbox environments for enterprise tools like Rapid7 and Sophos during the practical lab sections. No additional software purchases are necessary.
How long do I have access to the course?
Your enrollment includes ongoing access to the course and its available updates for the commercial life of the course or platform, subject to the Terms of Service.
Can I request a refund?
You may submit a request within 30 days. Approval is subject to the Refund Policy, including course progress, certificate, download, and account-use requirements.
Do I get a certificate?
Yes. Complete the required lessons and submit all required assignments to unlock your EmraSkills certificate of completion.
Can I preview lessons before buying?
When a preview is available, the lesson is clearly marked Preview in the curriculum so you can sample the teaching style before enrolling.